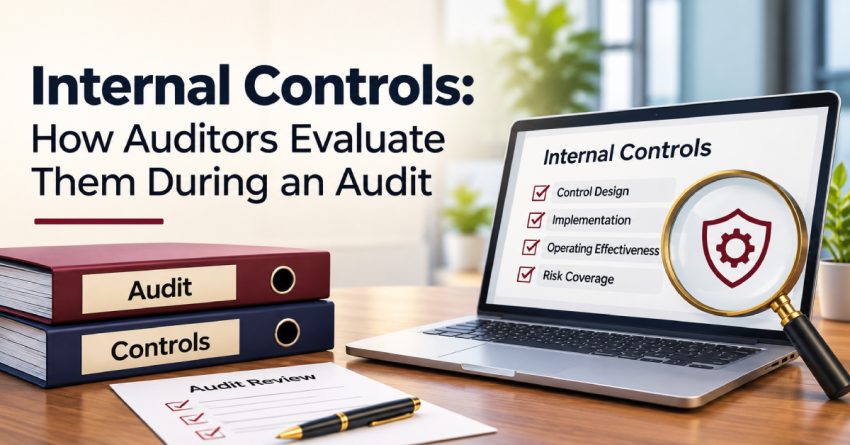
Internal controls help businesses safeguard their assets, maintain accurate financial records, and reduce the risk of errors and fraud. These controls include approval procedures, access restrictions, account reconciliations, and reviews of business transactions. During an audit, understanding how these controls operate helps auditors assess risks and determine the nature and extent of further testing required. Effective audit and assurance services can also help organisations identify control weaknesses and improve the reliability of financial reporting.
What Are Internal Controls?
Internal controls are the policies, procedures, and practices established by management to support effective operations, reliable financial reporting, and compliance with applicable laws and regulations.
For example, requiring management approval for significant payments, more than one person dealing with cash, restricted access to the financial system and periodic reconciliation of the bank account.
Internal controls can be considered as effective when employees adhere to them regularly.
Assessment of internal controls by Auditors
Auditors follow a systematic approach to understanding and evaluating an organisation’s internal control system.
Understanding the Control Environment and Procedures
Auditors begin by reviewing the organisation’s policies, procedures, and accounting systems.
This could be done by interviewing staff members, reviewing process documentation and observing transaction flow between departments.
This enables them to recognize important controls and the way errors are avoided or found within the enterprise.
Assessing Control Design
A control could be in place on paper but not be resolving the risk that it is designed to mitigate. Auditors thus evaluate if the control is designed properly.
If, for instance, large payments need to be authorised, this could limit unauthorised spending. But when the same person can do all three tasks – create the vendor, approve the invoice and release the payment – without any independent oversight, the process may have a significant control weakness.
Testing Control Effectiveness
Transactions and supporting documents, as well as approvals, system records and reconciliation statements may be selected for review by auditors. They may also watch procedures or perform specific checks to determine if controls have performed as they were expected to.
The nature and extent of control testing depend on the audit objectives, assessed risks, and applicable auditing standards. If controls are found to be ineffective, auditors may need to perform additional substantive procedures.
Evaluating Information Technology Controls
Numerous enterprises rely on accounting software and digital systems to handle financial data. They are able to review user access, system permissions, change management, and automatic checks.
Lack of access control may enable unauthorised modifications to the finances and poor system monitoring can make it more difficult to detect errors.
Common Internal Control Weaknesses Identified During Audits:
- Lack of segregation of duties.
- Missing or inadequate transaction approvals.
- Delayed bank and ledger reconciliations.
- Excessive access to financial transactions or systems.
- Inadequate documentation of control procedures.
Knowing these weaknesses enables auditors to analyze risk and decide on the need for additional investigation.
The Importance of Internal Control Evaluation
Evaluating internal controls is an important part of an audit because it helps auditors assess risks and determine the appropriate audit approach. It can also help management identify process gaps and areas where controls need improvement.
An audit does not, however, cover all controls and an audit opinion on financial statements does not imply that all the internal controls are effective.
Companies can get ready by documenting their processes, conducting regular reviews of access, performing regular reconciliations, and addressing weaknesses. A consistent approach reinforces accountability, aids in more consistent financial reporting and allows organisations to better manage financial and operational risk.
FAQs
Q: Why are internal controls important for businesses?
They help safeguard assets, maintain accurate records, reduce fraud or error risks, and support consistent business processes.
Q: What are common examples of internal controls?
Examples include payment approvals, restricted system access, segregation of duties, and regular bank reconciliations.
Q: How do auditors test whether controls are effective?
Auditors test selected transactions, approvals, system records, reconciliations, and documents to confirm controls operated as expected.